How Uncia works
Your whole estate in one base, with the answers that come with it
You connect your tools and complete them with your documents. Uncia turns it into the knowledge base of your whole IT estate, and you draw maps, outage impact, end-of-support dates and reports from it. It changes nothing in your systems.
What you connect, then what you drop in
Your tools as they are, with no integration project: connectors first, your files and documents to complete them.
- AWS AWS: accounts, machines, networks, rules
- Microsoft Azure Azure: subscriptions, machines, networks, rules
- Google Cloud Google Cloud: projects, machines, networks
- VMware VMware: sites, clusters, hosts, machines
- HHyper-V Hyper-V: hosts and machines
- Nutanix Nutanix: clusters and machines
- Kubernetes Kubernetes: clusters and workloads
- ServiceNow ServiceNow: the CMDB
- GLPI GLPI: inventory
- iTop iTop: repository
- Fortinet Fortinet: firewall rules
- Palo Alto Networks Palo Alto: firewall policies
- SStormshield Stormshield: firewall policies
- Zscaler Zscaler: user access paths
- Tenable Tenable: vulnerabilities
- Qualys Qualys: vulnerabilities
- Cyberwatch Cyberwatch: vulnerabilities
- Microsoft Intune Intune: endpoints
Plus all your data, structured or not: exports, architecture documents, PDFs, PowerPoint, diagrams, spreadsheets.
- Excel / CSV Spreadsheets: inventories, flow matrices
- Word Word: architecture documents
- PowerPoint PowerPoint: architecture documents and diagrams
- PDF PDF: documents and diagrams
- Visio Visio: diagrams
- draw.io draw.io: diagrams
- ArchiMate ArchiMate: models and diagrams
- C4 C4: diagrams
Connectors enabled according to your deployment scope. The brands mentioned belong to their owners.
-
Cloud
- AWS
- Microsoft Azure
- Google Cloud
AWS, Microsoft Azure and Google Cloud: machines, networks, managed databases, firewalls and rules, read by an account that cannot change anything.
-
Virtualisation and containers
- VMware
- HHyper-V
- Nutanix
- Kubernetes
VMware, Hyper-V, Nutanix and Kubernetes: sites, clusters, hosts, machines and workloads, organised the same way whatever the platform.
-
CMDB and inventories
- ServiceNow
- GLPI
- iTop
ServiceNow, GLPI and iTop: applications, owners and environments, checked against what the hypervisor and the cloud say. Every gap is raised.
-
Network and security
- Fortinet
- Palo Alto Networks
- SStormshield
- Zscaler
Fortinet, Palo Alto Networks, Stormshield and Zscaler: firewall rules, policies and access paths, checked against the required flows.
-
Vulnerabilities and endpoints
- Tenable
- Qualys
- Cyberwatch
- Microsoft Intune
Tenable, Qualys, Cyberwatch and Intune: known vulnerabilities and endpoints, tied to the machines and applications concerned.
-
Files and documents, to complete
- Word
- draw.io
- Visio
Exports, spreadsheets, flow matrices, Word or PowerPoint architecture documents, draw.io, Visio, ArchiMate, C4 and PDF diagrams. Diagrams are read and interpreted.
What Uncia does with it
It reconciles the sources: the machine seen by VMware, the row in the CMDB and the server in the architecture document become one element, with three sources.
Every piece of information is tied to a file, a date and a reference. When there is no source, it says so clearly.
When two sources disagree, both values are kept and the gap is shown for a decision.
When there is a doubt, Uncia asks questions.
The language model, Mistral Small 3 by default, reads documents on your servers, without going outside.
The metamodel is yours, and it can evolve with no code and no redeployment.
What you get
-
Connectors and sources
Your clouds, hypervisors, CMDB and firewalls connected read-only, your documents to complete them. Uncia says what it is missing.
Discover -
Mapping every layer
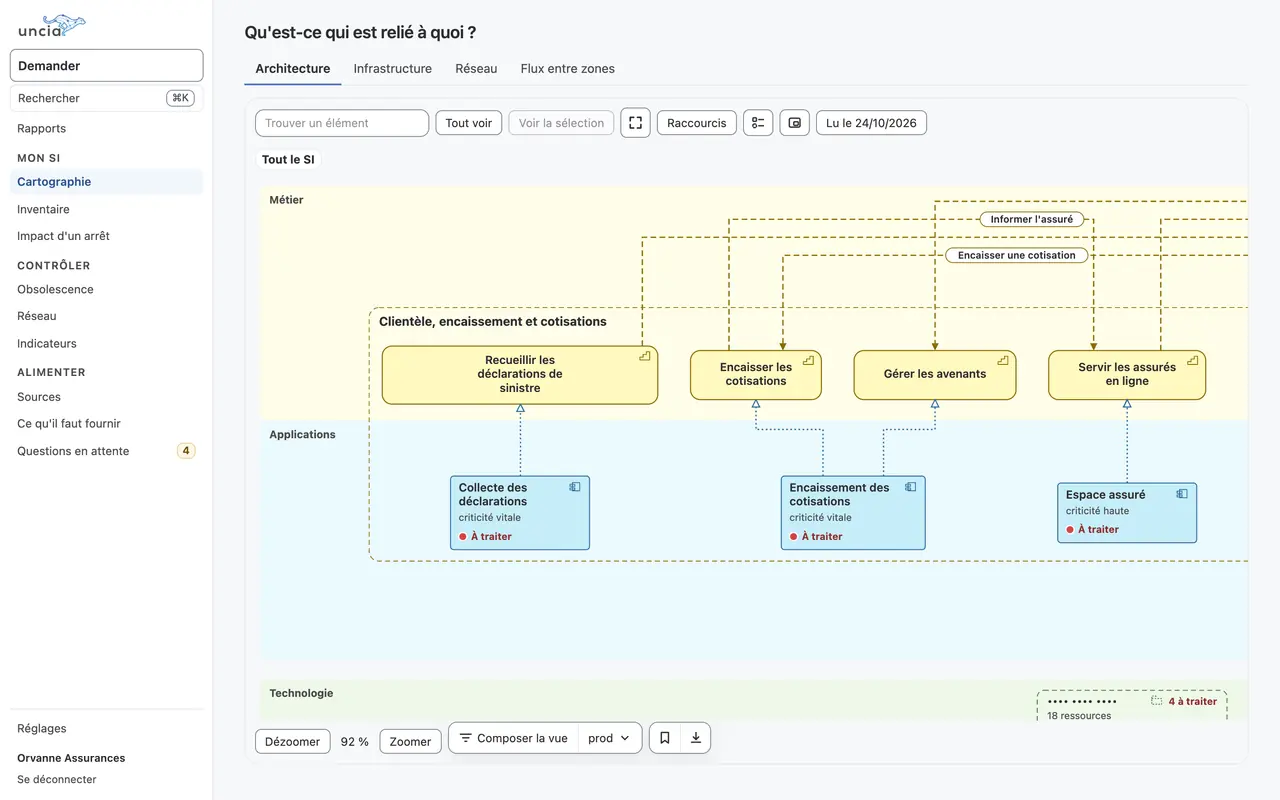
Generated maps, architecture, infrastructure, network, and the thread of an element from business to firewall.
Discover -
Architecture documents
Your architecture documents written and versioned in Uncia, existing ones imported and checked against reality, gap by gap.
Discover -
Compliance
Sourced inventory, flows checked against rules, reports structured along NIS2, DORA or ISO 27001.
Discover -
End of support and vulnerabilities
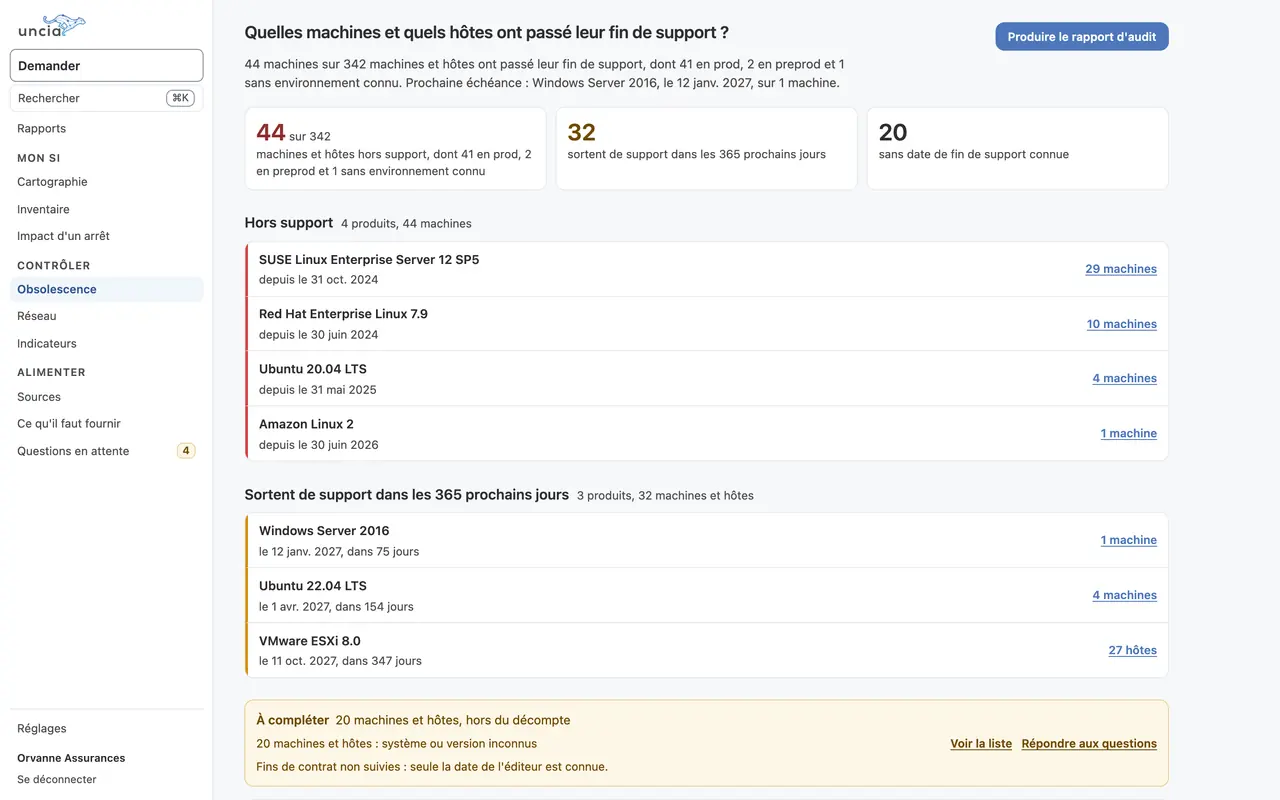
Dated, sourced end-of-support per product and per machine, cloud included, and the vulnerabilities identified in your estate.
Discover -
Run: impact, questions, reports
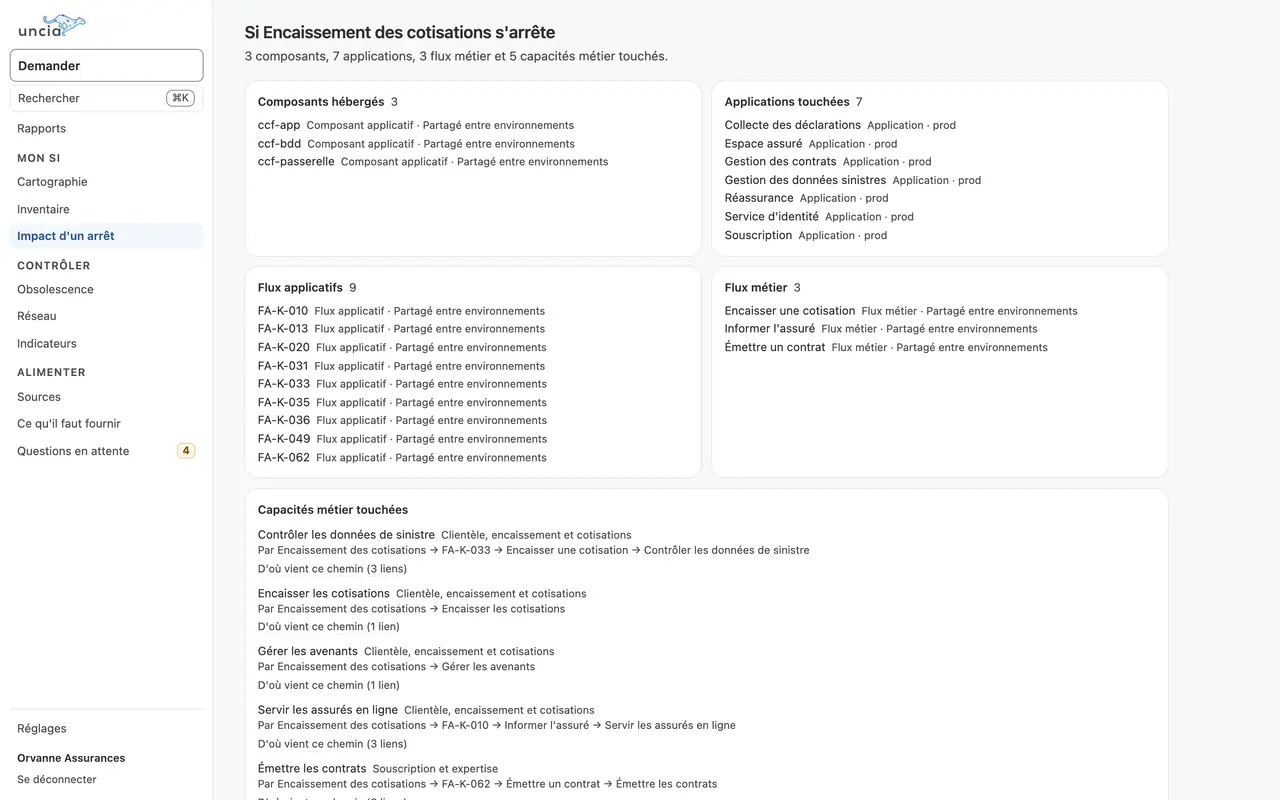
If this machine stops, what is the operational impact? Sourced answers, ready to export to Word or PDF for a committee.
Discover
The demonstration, in 8 screens
No account needed, on the demonstration base of a fictional insurer.
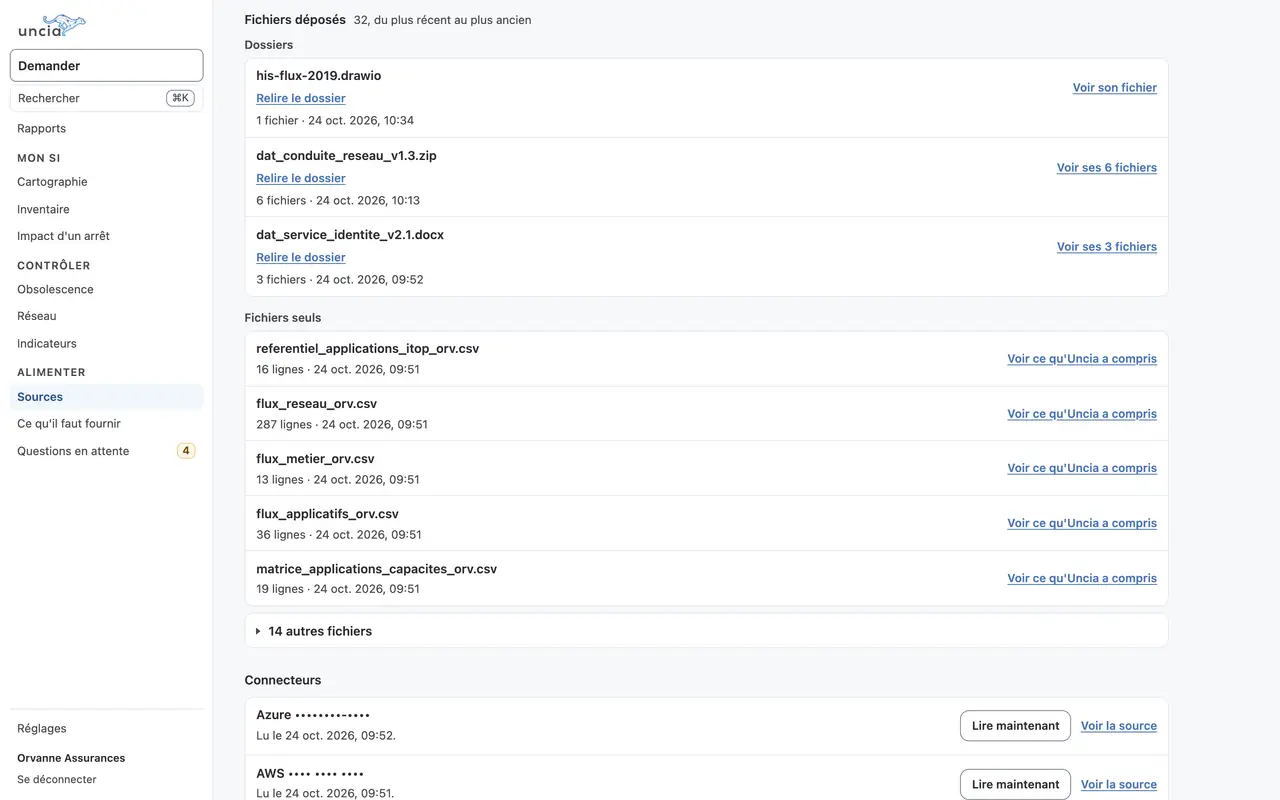
Connectors first: AWS and Azure, read by an account that cannot change anything.
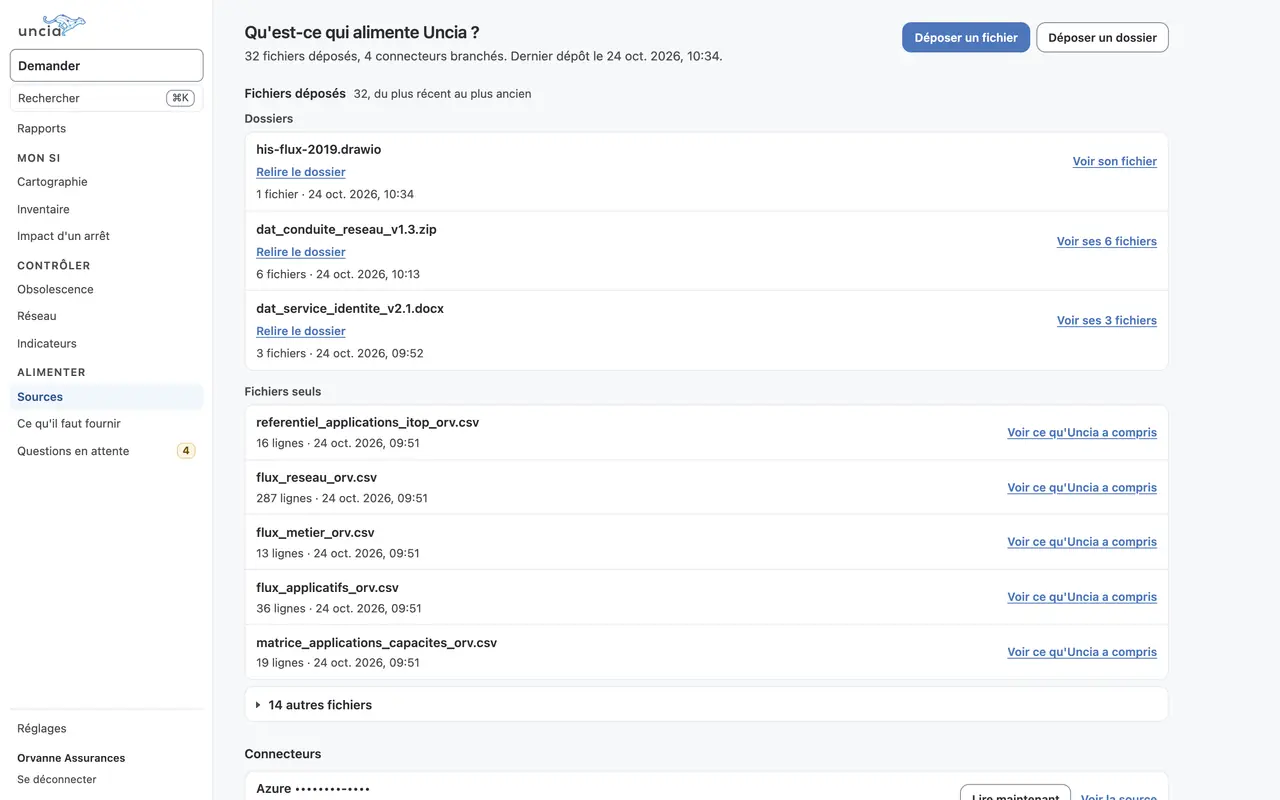
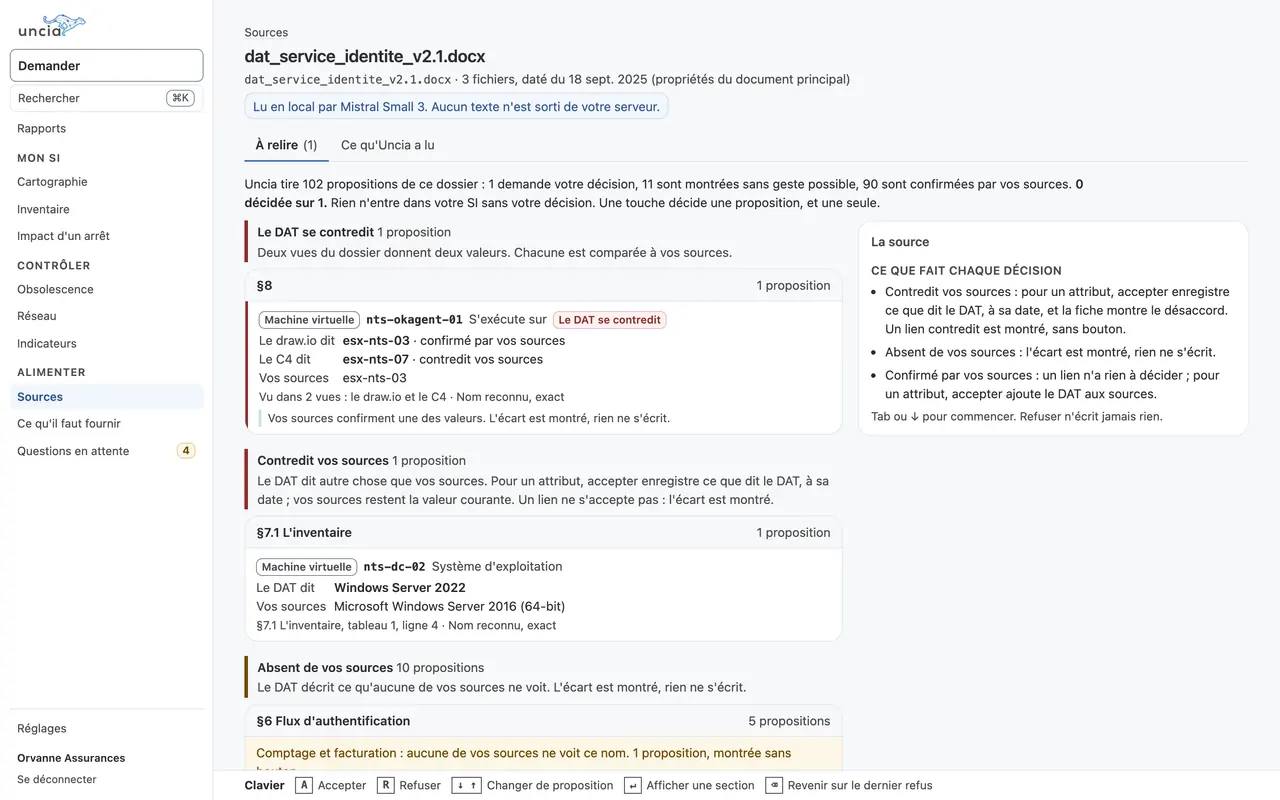
Connectors first: AWS and Azure, read by an account that cannot change anything.
See the same on your own estate →See your estate in Uncia in 30 minutes
We show you Uncia on a demonstration instance, then on part of your own estate if you wish: a read-only cloud account or a hypervisor export. You leave with a first map of that perimeter and a first view of your technical debt (end of support, gaps).